Insights
Expert insights on compliance, cybersecurity and data protection
50 articles
PCI DSS Regulatory Compliance 2026: Payment Card Industry Requirements & Audit Timeline
Decode PCI DSS regulatory landscape, mandatory compliance deadlines, and audit preparation steps for payment processors and merchants facing 2026 enforcement scrutiny.
PHP2Shell (CVE-2026-109618 & CVE-2026-109619): How to Patch PHP on Your Linux Servers
The 21 October 2026 PHP security release fixes two unauthenticated RCE flaws rated CVSS 9.2. Exact patch, restart and verification commands for Linux servers.
VAPT Tester vs. In-House Security Team: Cost, Timeline & Expertise Comparison 2026
Buyer-intent comparison guide: when to hire an external VAPT tester vs. building in-house capability, covering recruitment cost, timeline, and regulatory credibility gaps—tailored
HIPAA Compliant Software 2026: Features, Vendors & Compliance Checklist
Guide healthcare IT buyers through software selection criteria, vendor vetting, and audit readiness for HIPAA; positions SOC 2 as the trust signal vendors deliver to prove complian
Data Loss Protection (DLP) Software vs Data Leakage Solutions: 2026 Comparison Guide
DLP solutions are surging (+102% YoY) as enterprises tighten data governance. This guide compares endpoint, network, and cloud DLP tools and maps them to ISO 27001 A.46 (data leaka
Data Leak Protection vs Data Loss Prevention: Which Solution Your Business Needs in 2026
Clarifies the overlap between DLP and data leak protection, compares leading solutions (Tenable, Forcepoint, Varonis), and maps each to PCI DSS, GDPR, and HIPAA control requirement
GDPR Compliance Statement 2026: Essential Elements, Legal Templates & Audit Checklist
Buyers searching 'GDPR compliance statement' need clarity on mandatory disclosure language, data processing notices, and audit-readiness. Maps to DORA as both EU regulations increa
Data Loss Protection vs. DLP Software: What Actually Stops Breaches in 2026
Compares DLP solutions, deployment models, and ROI for enterprises preventing insider threats and accidental leaks—aligned to ISO 27001 A.13.2.1 and A.13.2.3 controls. Targets high
HIPAA Compliance Course vs. Self-Study: Which Approach Your Healthcare Team Actually Needs in 2026
Addresses the surge in HIPAA compliance course searches by comparing formal training programs against DIY approaches, positioning Praxis-Q as the trusted guide for healthcare organ

Network Firewall Security for ISO 27001 Compliance: Implementation & Control Mapping 2026
Explores how firewalls map to ISO 27001 A.13 boundary protection controls and act as foundational infrastructure for compliance audits. Targets organizations building or auditing t
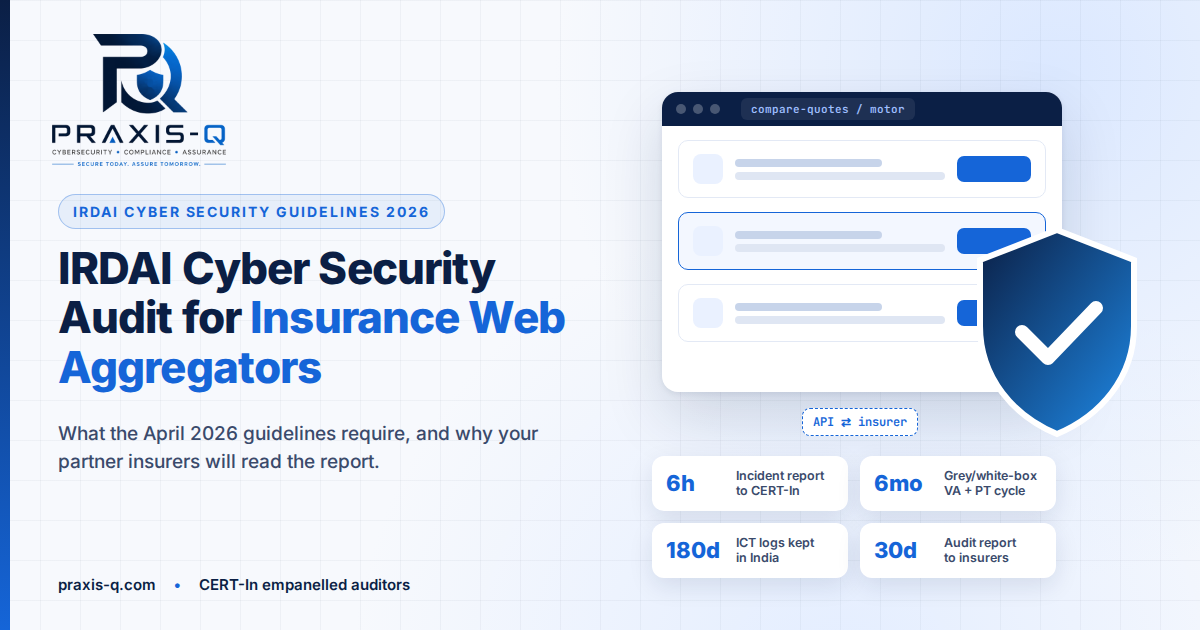
IRDAI Cyber Security Audit for Insurance Web Aggregators: 2026 Guide
What IRDAI's April 2026 cyber security guidelines require of insurance web aggregators: annual audit, six-monthly VAPT, 6-hour reporting, and reports to insurers.

HIPAA Compliance Training vs. Self-Study: What Healthcare Organizations Actually Need in 2026
HIPAA training demand is up 2.3x YoY. This post compares managed training programs to DIY approaches, positioning Praxis-Q's fast-track delivery as the faster compliance path for h
SIEM Total Cost of Ownership: What Actually Drives the Bill
The licence is rarely the largest line. Storage across the retention window, tuning effort and the analyst who reviews the alerts are what decide a SIEM budget - and the seven numbers to have before anyone quotes anything.
Wazuh Mapped to ISO 27001, SOC 2 and PCI DSS: What Each Module Actually Evidences
Which Wazuh capability produces which audit artefact, for which control, and what the tool does not cover. ISO/IEC 27001:2022 Annex A, SOC 2 Trust Services Criteria and PCI DSS v4.0.1 Requirement 10.
Open-Source SIEM Compared: Wazuh, Graylog, Elastic and Security Onion
Wazuh, Graylog, Elastic/OpenSearch and Security Onion do not do the same job. An honest comparison of what each is built around, where each hurts, and the four questions that actually decide the choice.

VAPT vs Penetration Testing: Cost & Scope Comparison for Bangalore Businesses (2025)
Merge two striking-distance queries (VAPT pos 19.7, pen-test pos 30) with buyer-intent comparison; clarify scope, pricing, and Praxis-Q's fast-track advantage for tech hubs.

ISO 27001 Certification in Mumbai, Pune & Hyderabad: Region-Specific Fast-Track (2025)
Consolidate 3 high-intent city queries (pos 24–27, 28–41 impressions) into one comparison post showing timeline, cost, and local audit body contact; drive traffic to Mumbai money p

NIST CSF vs. ISO 27001 vs. SOC 2: Which Compliance Framework Does Your Business Need in 2026?
Close the competitor gap on foundational compliance comparisons (6 competitors ranking on NIST CSF, PCI DSS, HIPAA, SOC 2) by authoring the definitive multi-framework decision tree

ISO 27001 Certification Cost & Timeline: Mumbai vs. Pune vs. Hyderabad vs. Chennai (2026)
Address 31–44 impressions on city-specific ISO 27001 queries (Mumbai, Pune, Hyderabad, Chennai, Delhi) with a transparent pricing & timeline comparison, directly competing for 21–2

EDR vs XDR vs MDR: What Indian Businesses Actually Need in 2026
EDR watches endpoints, XDR correlates endpoints with identity, email and cloud, and MDR is a service running one of them for you. How to choose on headcount, what CERT-In six-hour reporting and 180-day in-India log retention force into the decision, and the seven questions that separate real capability from a demo.

How to Verify an ISO 27001 Certificate Is Genuine
A genuine ISO 27001 certificate names an accredited certification body, a certificate number, a real ISMS scope and an expiry date — and appears on the certification body's register or IAF CertSearch. Four checks, the red flags that matter, and what to do when a supplier's certificate fails.
IRDAI Cyber Security Rules for Insurance Intermediaries: 2026 Guide
IRDAI's 2026 cyber security guidelines for brokers, TPAs, corporate agents and aggregators: annual audit, reports to insurers, six-monthly VAPT and a 6-hour reporting rule.
IRDAI Cyber Security Audit Checklist for Insurers: 2026 Guidelines
What IRDAI's April 2026 cyber security guidelines change for insurers: quarterly ISRMC, an independent CISO, rotated auditors, six-monthly VAPT and a 90-day filing.

Application Security Testing for Canadian SaaS: PIPEDA vs. Bill C-26 Compliance Checklist
Fill Canada gap: 'application security testing canada' (pos 13.6, 41 impr) is under-ranked; reframe as a compliance + security decision for SaaS founders navigating PIPEDA + Bill C

CSITE Audit vs. CSITE Investigation: What Indian Banks & Fintech Must Know (RBI Compliance 2026)
Clarify confusion: 'CSITE audit' (pos 5.9) and 'RBI CSITE audit' (pos 9.4) cluster at 235–33 impressions but lack clear definition—position Praxis-Q as the expert guide differentia

ISO 27001 Certification in India: 5-City Comparison + Fast-Track Timelines (2026)
Consolidate 5 high-impression city queries (Hyderabad 48, Pune 37, Mumbai 34, Chennai 31, Delhi 15) into one comparison guide with Praxis-Q's fast-track differentiator; positions a

Praxis-Q Achieves ISO 9001:2015 and ISO/IEC 27001:2022 Certification
We just became ISO 9001:2015 and ISO/IEC 27001:2022 certified ourselves, audited by QRO and accredited by EGAC under the IAF Multilateral Recognition Arrangement.

PCI Compliance Levels for Merchants and Service Providers
Understand PCI DSS compliance levels for merchants & service providers. Level 1-4 requirements vary by transaction volume. Learn your level, audit timeline & security obligations.

How to Create an Effective Business Continuity Plan
A robust business continuity plan ensures your organization survives disruptions. Learn 5 essential steps to create an effective BCP aligned with ISO 27001 standards in India.

How to Choose the Right PCI SAQ for Your Business
Navigate PCI SAQ selection with confidence. Learn which questionnaire fits your business model, reduce compliance scope, and accelerate your DSS certification process.

Cloud Security Posture Management (CSPM) Explained
Cloud Security Posture Management (CSPM) continuously monitors & remediates cloud infrastructure misconfigurations. Learn how CSPM integrates with VAPT for comprehensive cloud security in India.

Zero Trust Architecture: A Practical Implementation Guide
Zero Trust Architecture eliminates implicit trust in networks. Learn practical implementation strategies aligned with VAPT testing, India's RBI SAR compliance, and modern cybersecurity frameworks.

RBI CSITE Audit Checklist 2026: Requirements & Cost
A practical checklist covering RBI CSITE audit requirements, cost, and how banks and NBFCs can fast-track compliance in 2026.

SOC 2 Type 2 vs Type 1 Audit: How to Choose in 2026
SOC 2 Type 1 and Type 2 audits serve different purposes. This guide compares scope, cost, and timeline to help you choose the right one for your business.

VAPT vs Vulnerability Scanning: When to Use Each Test
VAPT and vulnerability scanning aren't interchangeable. This guide explains when each security test is appropriate in a 2026 enterprise security program.

SOC 2 Type 2 vs PCI DSS: Which Do You Need in 2026?
SOC 2 Type 2 and PCI DSS serve different purposes but often get compared. This guide clarifies the differences so you can pick the compliance path that fits.

ISO 27001 Certification Cost in India (2026)
ISO 27001 certification in India costs ₹1.5–2.5 lakh all-in for 10–50 staff and ₹3–4.5 lakh for 50–200, including the accredited certification body fee.

PCI DSS Compliance Roadmap: Pune, Bangalore & Hyderabad
A practical PCI DSS compliance checklist for fintech and payment firms in Pune, Bangalore, and Hyderabad, covering 2026 requirements step by step.

SSAE 18 Report vs SOC 2 Type 2: Cost & Timeline (2026)
SSAE 18 and SOC 2 Type 2 serve overlapping purposes but differ in cost, timeline, and scope. Here's how to decide which report your vendors actually need.

RBI CSITE Audit vs ISO 27001: Which Do You Need in 2026?
RBI's CSITE audit and ISO 27001 certification overlap but aren't the same. This guide clarifies which applies to your sector, cost, and timeline.

NIST CSF Assessment Checklist: Implementation Guide 2026
A practical checklist for assessing your organization against the NIST Cybersecurity Framework (CSF) and turning its principles into concrete actions in 2026.

What Is SSAE 18 Reporting? A Complete Guide (2026)
SSAE 18 is the reporting standard behind most SOC 2 audits. This complete guide explains what it covers and why it matters for service organizations in 2026.

PCI DSS Compliance Checklist 2026: Cost & Fast-Track
A practical PCI DSS compliance checklist for 2026, covering cost, scope, and the fastest realistic path to certification for payment processors and merchants.

SOC 2 Security Awareness Training: Managed vs DIY (Cost & Risk)
Managed SOC 2 security awareness training costs 40-60% more but cuts breach risk by 80%. DIY saves $15K-30K yearly but demands expertise. Compare strategies for your compliance posture.

ISO 27001 Audit Checklist: Security Awareness Training Requirements
Master ISO 27001 security awareness training audit requirements. Our checklist covers mandatory controls, assessment methods & compliance documentation for fast-track certification.

Security Awareness Training Program: Timeline, Cost & Scope FAQ
Learn security awareness training program timelines, costs & scope. Fast-track implementation in weeks with CISA-certified assessors. Complete FAQ guide.

Internal Audit vs CERT-In Empanelled Partner: Cost & Timeline Breakdown
CERT-In empanelled audits cost ₹3–8L & take 4–6 weeks vs internal audits costing scoped per engagement over 8–12 weeks. Fast-track certified assessors deliver compliance in weeks, not months.

DIY Security Awareness Training vs. Managed Programs: Cost-Benefit
DIY security awareness training costs less upfront but managed programs deliver 3-5x ROI through expert design, compliance expertise, and measurable risk reduction. Compare costs today.

CERT-In vs ISO 27001: Which Audit Does Your Org Really Need?
CERT-In audit mandatory for Indian orgs; ISO 27001 globally recognized. Learn which compliance framework fits your risk profile, regulatory sector & international expansion goals.

CERT-In Empanelled Audit: Cost, Timeline & Scope FAQ for CISOs
CERT-In audit cost: scoped per engagement depending on org size. Timeline: 4-8 weeks. Scope covers critical infra, data security, incident response. CISO FAQ inside.